 Do Son
Currently, cybersecurity is one of the biggest headaches for any business operating online. From banks to online stores, etc., you must be alert 24/7 to defend against mirage of attacks aimed at you.
One of the first steps you can take to defend against dangerous online attacks like the Man in The Middle Attacks (MiTM), is to buy the best Secure Socket Layer (SSL) certificates. The market is however loaded with SSL certificate vendors and digging through the web pages to find a legitimate dealer can be a bit mind-numbing.
Nevertheless, if you’re looking for a cheap SSL for your website, we got your back!
In this article, we bring a reputed name called SSL2BUY review, that could be fit with your SSL requirement. We have mentioned a few points about this SSL provider so, let us walk through them;
- The introduction of Web security, SSL and why it’s crucial.
- The types of SSL certificates.
- Features and benefits of SSL2BUY
The Introduction of Web Security and SSL
Long gone are the days when hackers only targeted larger businesses and guessed login details to access databases. Today they focus every business making 60 percent of startups to close businesses in under six months after an attack.
The online thieves use sophisticated automated software that cleverly marks all vulnerable sites so they can launch attacks. Therefore, the best bet is to invest in high-end web security systems that will keep off the hackers.
As part of the web security efforts to tame the online attacks, SSL was introduced. The sole aim was to secure online transactions between businesses and their target consumers.
Over time it has gone several changes, and today the certificates are available in different types and forms to match various needs.
About SSL2BUY:
When looking for the best SSL certificate to buy, you must pay attention to the features like ease of use and support, etc. They’ll help you avoid little headaches when installing or using the certificates on your site.
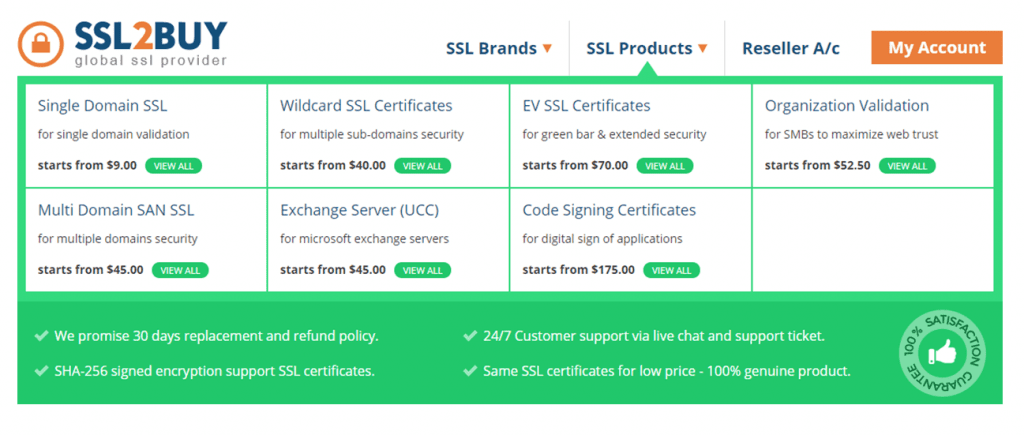
One of the reputable SSL vendors is SSL2BUY. It’s an authorized vendor providing a wide variety of SSL certificates at reasonable market prices to secure websites for organizations, startups, and individuals.
It also partners with major Certificate Authorities (CAs) like Symantec, Comodo, GeoTrust, RapidSSL, Thawte and GlobalSign to offer reliable services when it comes to securing businesses online. SSL2BUY guarantees a 100 percent satisfaction rate and backs this up with a 30-day money-back guarantee for unsatisfied clients.
It also has the best customer support that’s available 24/7 to help you manage any issue you could be facing when using the product.
Why You should choose SSL2BUY?
SSL2BUY is a global provider of the SSL certificates. Most businesses like it because of its benefits mentioned as under;
• It’s cheap.
• It offers 24/7 customer support round the clock.
• It’s an authorized reseller for popular SSL Certificate Authority like Symantec, Comodo, GeoTrust, RapidSSL, Thawte and GlobalSign etc.,
• All the certificates come with a 30-day money-back guarantee.
• It’s a global company serving over 65 countries.
• The prices of SSL products are unique and set to accommodate the different business budget.
• It earned 4.8/5 reviews based on more than 11,000+ satisfied customers.
Types of SSL Certificates
There are six types of SSL certificates. When you install a certificate on your site, the web URL will change from HTTP to HTTPs.
After this, you’ll notice a padlock sign in your address bar, which is vital in helping you build the trust with your web visitors. SSL certificates will not only help you enhance your site’s security, and reputation but also boost your SEO rankings.

Here’s a brief on the six types of SSL certificates
- EV SSL (Extended Validation Certificates)
This is typical, the most expensive SSL certificate with the essential features. When you install the EV SSL certificate on your site, it will indicate your business name and the padlock sign on the address bar.EV SSL is a popular option for enterprises that are looking to distinguish themselves from insecure sites. It’s a must-have for sites which store or collect online payments and process sensitive data like login details etc. E-commerce, banking, financial sites prefer such type of certificate.
- Organization Validated (OV SSL)
The OV SSL is designed to encrypt the website user’s sensitive data when performing transactions online.It’s also a must-have for public or commercial websites to ensure that all the customers’ details shared on the site remain private. Enterprise who wants to verify their business identity over the web, OV SSL is preferable SSL for them.
- Domain Validated (DV SSL)
The DV SSL is a recommendable option for newbie, small budget base website, informational websites, and blogs. It carries minimal issuance process and the strong encryption that comes with it.It’s straightforward to obtain, and when installed, it will show only the HTTPS plus the padlock sign. It doesn’t show the business name in the address bar. This SSL confirms that the domain owner is verified and has the right to use it.
- Wildcard SSL
Wildcard SSL will help you to secure a base domain plus numerous other first-level subdomains. It’s a cheaper option when compared to buying different single-domain SSL certificates.You can also buy an OV Wildcard SSL and DV Wildcard SSL. On purchase, they come with an asterisk* which stands for a valid subdomain of the base domain. The vendor assures about cheap wildcard SSL in the SSL industry.
- Multi-domain SSL
This SSL certificate is designed to secure multiple domains up to 250 domains with one certificate (may vary from vendor to vendor). It allows you the freedom of easily modifying the Subject Alternative Name (SAN) and deleting or changing your SANs the way you wish. If you have multiple domains/subdomains, then, this SSL is like a boon. It also saves extra cost invested in purchasing a different SSL certificate. - The Unified Communications Certificate (UCC SSL)
The UCC SSL certificates are also referred to as multi-domain SSL. It is a popular option when it comes to secure Live communications and Microsoft Exchange Services like OWA, auto-discover, SMTP, etc. It is available for all webmasters to secure multiple domain names under one certificate.When activated and installed they indicate the HTTPS plus the padlock sign on the web browser URL.
Here’s a simple rundown of overall features of SSL products from SSL2BUY:
- SHA-2 Algorithm.
- Data security.
- 30-day money-back guarantee.
- Unlimited SSL reissuance
- Password and access control.
- API feature for resellers.
- 256- Bit SSL encryption.
- 24/7 hour customer support.
- 2048- Bit CSR encryption.
- Unlimited server licenses
Certificate Authorities Tied Up:
SSL2BUY offers diversified products at an excellent price from different certificate authorities (CAs). There are many in-demand products from CAs that are discussed below.

Comodo: Comodo being a security leader, has many SSL certificates categorized for different size of businesses. The popular products include Positive SSL, multi-domain SSL, which prices start from $9/yr. and $45/yr. Respectively.
GlobalSign: GlobalSign offers single domain SSL, Organization SSL, Wildcard, and EV SSL certificates that are a bit high in price compared to Comodo authority. The price range starts from $109.50 that may reach up to $525/yr. — depending upon the certificate type. The in-demand product is GlobalSign Domain SSL.
Symantec Group: Symantec Group consists of RapidSSL, GeoTrust, Thawte, and Symantec. Whether it is RapidSSL, ThawteSSL123, or GeoTrust TBID SSL, all these products are popular among customers, and their prices vary upon different brands and types of SSL certificates.
AlphaSSL: AlphaSSL being one of the trendy products in SSL2BUY, offers a single domain and wildcard SSL Certificate, which prices are $17.50/yr. and $40/yr.
Conclusion
SSL2BUY is a global leader when it comes to SSL certificates issuance and services. It provides some of the best features in the SSL products that will unarguably meet all your needs. The cheap pricing plans also make it a viable option for businesses of different sizes.