
 Do Son
Acronis ties a new PATCHCORD malware APT36 campaign to Afghan telecom and Indian targets. SHEETCORD malware abuses Google Sheets for C2.
Transparent Tribe
SHEETCREEP malware is a C# Google Sheets RAT tied to APT36. It hides command-and-control inside Google Sheets to evade network detection.
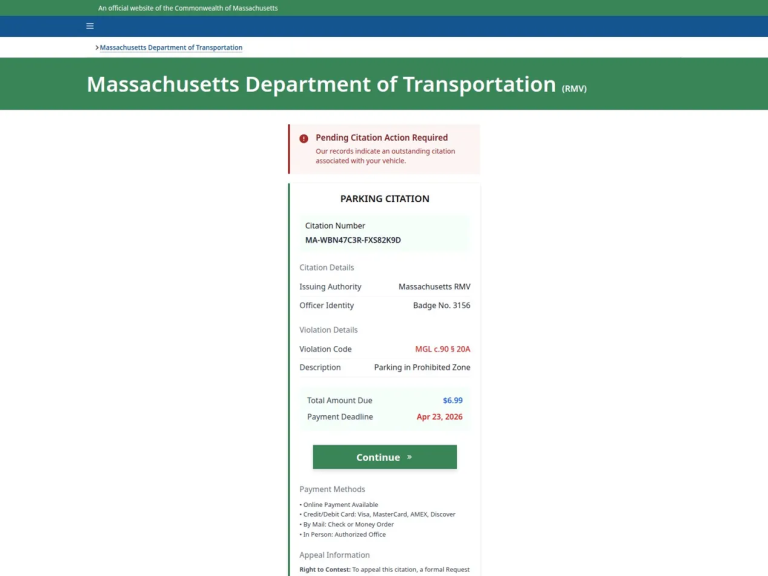
Cyble uncovers "Operation Trust Trap," a 16,800-domain network weaponizing *.gov trust to steal credentials. See how APT36 and others hijack the human eye.

CYFIRMA reveals a new cyber espionage campaign by Transparent Tribe (APT36) targeting Indian defense with stealthy multi-stage malware and decoy PDFs.
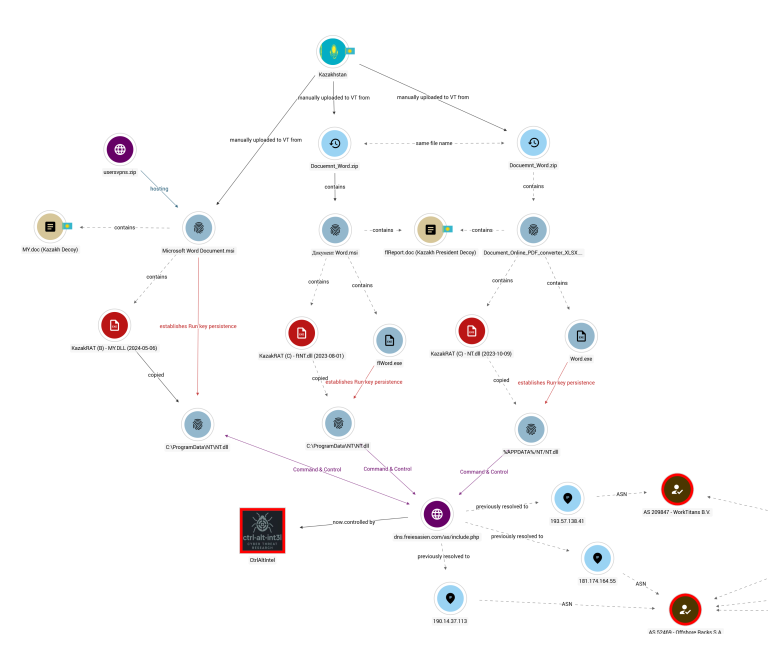
Researchers uncover "KazakRAT," a state-affiliated spyware targeting Kazakhstan & Afghanistan. A lapsed domain allowed experts to sinkhole the C2.
CYFIRMA unmasks APT36's latest campaign: a fake JLPT exam lure using fileless LNK malware to evade antivirus and spy on Indian government targets.

CYFIRMA exposes APT-36 weaponizing a fake NCERT WhatsApp advisory to deliver a stealthy backdoor and seize long-term control of government systems.

Transparent Tribe (APT36) evolves with new Linux malware targeting Indian government BOSS systems via weaponized shortcut files.

A new report reveals that the Pakistan-based APT36 is targeting Indian government entities using spear-phishing and Linux-specific malware to steal sensitive data.
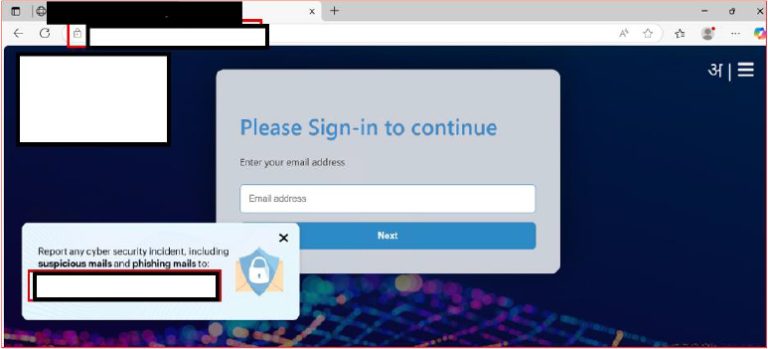
APT36, a Pakistan-linked threat actor, is targeting Indian government officials with phishing campaigns that mimic official websites to harvest credentials and Kavach MFA OTPs in real time.

A new report reveals APT36 (Transparent Tribe) is escalating cyber-espionage against India, using phishing and .desktop files to deploy the Poseidon backdoor for long-term access.
APT36 (Transparent Tribe) is now targeting Indian government agencies via BOSS Linux with spear-phishing. It uses malicious .desktop files to deploy Go-based malware for espionage.

APT36 is targeting Indian defense personnel with sophisticated phishing, using fake NIC documents and multi-layered malware to steal sensitive data and evade analysis.

DRAT V2, a new Delphi-compiled RAT from TAG-140 (SideCopy/Transparent Tribe), is targeting Indian government entities with expanded post-exploitation and refined C2 techniques.
A sophisticated phishing campaign, possibly by APT36, spoofs Indian government sites and uses ClickFix tactics to target Windows and Linux users.
Seqrite Labs uncovers APT36 phishing campaign using Pahalgam terror attack-themed lures to deploy Crimson RAT against Indian government targets.

Uncover the stealthy techniques threat actors are using: LNK files and SSH commands in advanced cyberattacks.

Uncover the secrets of Secret Blizzard, a Russian threat actor known for hijacking other groups' infrastructure for intelligence gathering.

Learn about the evolution of ElizaRAT and how APT36 has refined its malware to target high-profile entities in India.
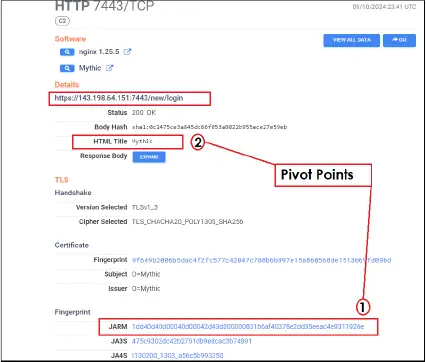
Uncover the activities of Transparent Tribe APT group and their new tactics of espionage. Learn how they target Indian government officials and defense sectors.
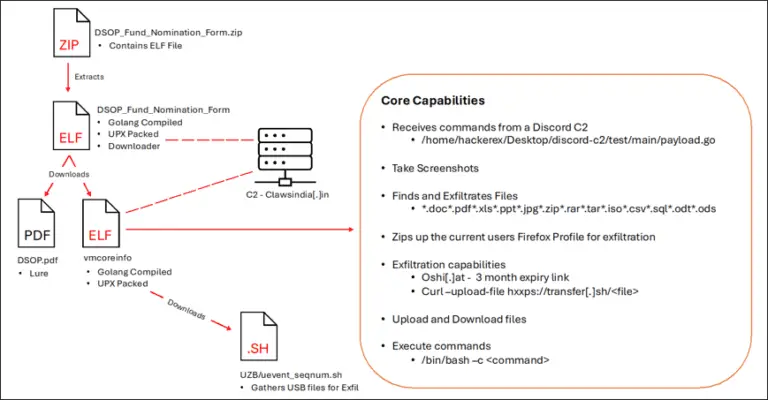
Researchers revealed a sustained campaign by Pakistani-based cyber espionage group APT36 targeting critical Indian government
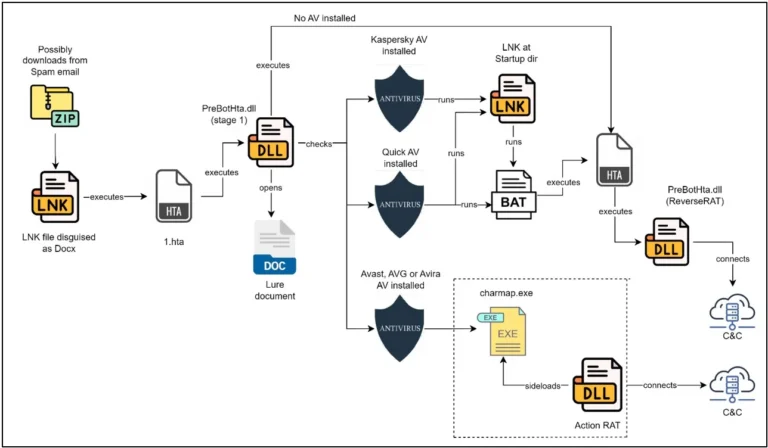
Upon further investigation, CRIL uncovered the use of malicious LNK files in the SideCopy malware campaign. These files, once executed